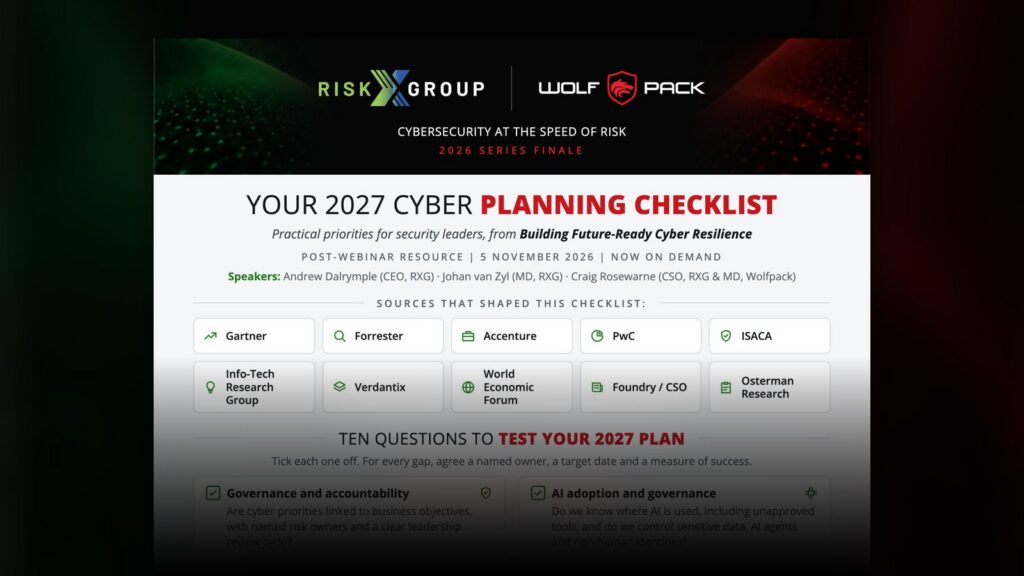
Most 2027 security plans are being signed off now. This one-page checklist gives security leaders ten questions to test that plan before it goes to the board, drawn from the 2026 series finale webinar Building Future-Ready Cyber Resilience.
Each question covers one area where plans most often fall short. Tick off the ones you can answer with confidence. For every gap, agree a named owner, a target date and a measure of success.
What the checklist covers
- Governance and accountability
- AI adoption and governance, including unapproved tools, AI agents and non-human identities
- Skills and specialist capacity: build, recruit, or source through a vCISO or specialist support
- Penetration testing and validation
- Security operations and response
- Third-party and supply chain risk
- Incident readiness and recovery
- Awareness and human risk, including AI-enabled fraud
- Data, identity and infrastructure, including connected IT and OT
- Budget and tool optimisation
The questions draw on research from Gartner, Forrester, Accenture, PwC, ISACA, Info-Tech Research Group, Verdantix, the World Economic Forum, Foundry / CSO and Osterman Research.
About the webinar
Building Future-Ready Cyber Resilience closed the 2026 Cybersecurity at the Speed of Risk series with Wolfpack on 5 November 2026, and is now available on demand. See the webinar details or watch the recording.
Speakers: Andrew Dalrymple, CEO, Risk X Group; Johan van Zyl, Managing Director, Risk X Group; and Craig Rosewarne, CSO, Risk X Group, and Managing Director, Wolfpack.
Need help closing the gaps?
Risk X Group helps security leaders prioritise requirements, build a defensible budget and source specialist capacity, from vCISO support to testing, SOC and response. Book a meeting or ask us for the 2027 CISO Budget Dashboard.